[FoxNews] More than 220 providers were terminated after investigators found billing for more than 24 hours of services in a single day
Florida's sweeping Medicaid fraud crackdown has helped drive a nearly $1 billion reduction in projected annual spending on behavioral therapy services alone, according to state officials, after investigators uncovered suspicious billing practices.
Tallahassee’s internal crackdown — which included discoveries of providers billing Medicaid for more hours than there are in a day — comes amid heightened federal scrutiny of Medicaid fraud, including investigations and payment reviews involving Minnesota.
The DeSantis administration said its approach aims to stop suspicious Medicaid claims before taxpayer dollars are paid out rather than trying to recover improper payments afterward. The strategy mirrors a call from HHS Secretary Robert F. Kennedy Jr. to move away from traditional "pay-and-chase" models.
More than 220 Medicaid providers have been terminated for fraud, waste or abuse, while more than 260 have faced payment restrictions or suspensions. The state has also referred more than 150 suspected fraud cases to the attorney general's office over the past year.
Annual Medicaid spending on Applied Behavior Analysis (ABA), a therapy commonly used for children with autism, had been projected to reach $3.86 billion but is now expected to total $2.88 billion in fiscal year 2026-27, according to the governor's office. Officials attributed the nearly $980 million reduction to a combination of fraud enforcement, managed care and utilization management efforts.
Florida's Agency for Health Care Administration (AHCA) told Fox News Digital that its expanded monitoring uncovered providers billing Medicaid for services through every weekend and holiday for months, including instances in which providers billed for more than 24 hours of services in a single day.
"Protecting Medicaid means protecting the people it was created to serve," AHCA Secretary Shevaun Harris said in a statement.
"For children, pregnant women, the disabled, and our seniors, it means making sure they have access to high-quality care while ensuring taxpayer dollars are not lost to fraud or abuse. AHCA will continue taking decisive action to strengthen program integrity, hold bad actors accountable and safeguard these critical services for Floridians," she said.
Harris’ agency provided additional details on its crackdown to Fox News Digital, including how its new fraud-protection mechanisms work.
Through a pilot program with identity-verification firm SentiLink, Florida is screening for stolen or fake identities and hidden ownership structures among Medicaid providers. Separately, the state has imposed enrollment moratoriums on certain high-risk provider categories.
AHCA also told Fox News Digital that it has issued more than 1,000 adverse decisions involving Medicaid provider enrollment or re-enrollment since January 2026, part of its effort to prevent suspicious providers from entering or remaining in the program.
The agency has conducted 400 site visits to providers since January, including providers in high-risk categories such as applied behavior analysis, medical equipment and adult day care.
"Medicaid fraud is a national problem, and it is growing more sophisticated everywhere," AHCA told Fox News Digital.
"Florida is not waiting to be told what to do. We are building the model: prevent fraud at the front door, verify every provider, and follow the data. We welcome partnership with CMS and other states, because a fraudulent provider stopped in Florida is a scheme that does not move on to the next state."
[Breitbart] Tragedy struck Mexico this week when professional wrestler El Hijo de Fishman, 36, allegedly killed veteran referee Gerardo German Pineda, 75, while performing a piledriver on him.
Police have since arrested Fishman on manslaughter charges following the referee’s death, which occurred during his matchup against Mascara Sagrada in Hidalgo for the El Patrón Espectáculos Lucha Libre promotion.
After Fishman performed the signature wrestling move on Pineda, he reportedly became immobile and was later pronounced dead. The move involves the wrestler appearing to drop the target vertically onto their head, creating the illusion of a slam while the wrestler’s body absorbs the shock to keep the head from hitting the mat. Professional wrestlers have often discussed how to perform the move safely in tutorials:
#2
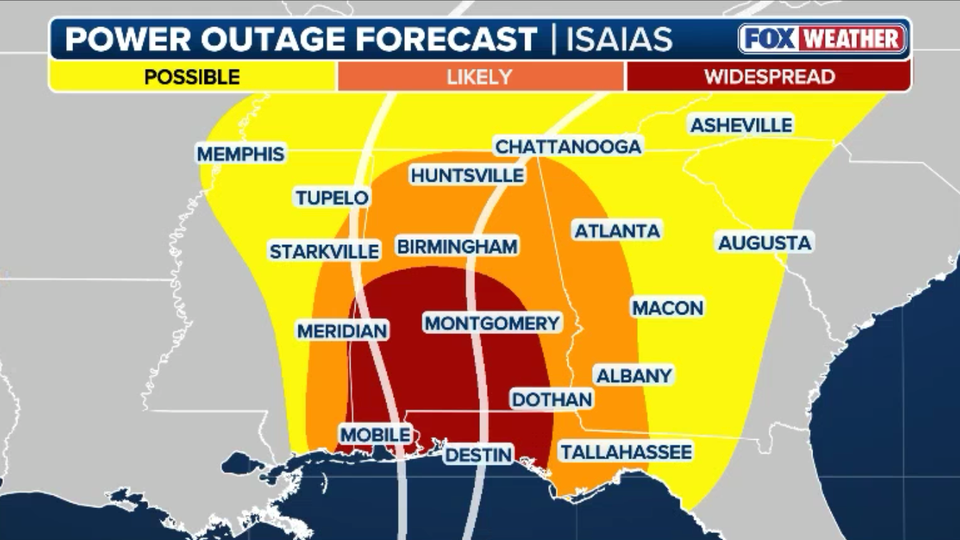
Pensacola, Florida bracing for Hurricane Isaias' impact Pensacola Mayor D.C. Reeves joins Fox News to discuss evacuations and storm preparations as Hurricane Isaias threatens the Gulf Coast. Florida Gov. Ron DeSantis warns residents to prepare for heavy rainfall and storm surges.
Pensacola Mayor D.C. Reeves warns residents along the Gulf Coast to prepare for Hurricane Isaias. The Category 2 storm brings winds of 110 mph, prompting evacuations and emergency preparations across the region. Local officials urge communities to secure homes and gather essential supplies before the hurricane makes landfall.
#3
Need to get any expensive aircraft at NAS Pensacola somewhere else.
Regarding storm surge, at this point it is likely the center of the storm will pass east of Pensacola so Pensacola will get somewhat weaker winds then further east but its good to prepare for something worse than you expect.
Posted by: Lord Garth ||
10/09/2026 12:47 Comments ||
Top||
[Breitbart] Multiple federal agencies announced on Wednesday that they had seized 90 shipments of fuel illicitly intended to be sent from the United States to a sanctioned corporate entity in Cuba.
The shipments, which reportedly mostly contained diesel fuel, were reportedly valued at $2.8 million and expected to be received by the Cuban energy corporation ENETEC S.A., which the U.S. government sanctioned due to its role in funding the illegitimate communist regime in control of that country. The federal agencies stated that the shipments seized were preparing to depart from Florida and Texas.
The seizure reveals that American authorities believe that the Cuban regime, desperate for petroleum products, is apparently seeking them in the United States despite the long-established alleged “embargo” limiting commercial activity with the Castro family dynasty. Cuba has been experiencing severe fuel shortages this year following the arrest of Venezuelan dictator Nicolás Maduro in January, who for years provided free or heavily discounted fuel to Cuba in exchange for political and military support.
Cuba especially needs access to diesel and other petroleum products because its dilapidated power grid cannot sustain the nation’s electricity demands. As a result of over half a century of socialist mismanagement, Cuba barely maintains a power grid and what is left of it routinely fails; the wealthy, tourists, and communist elites became accustomed to accessing electricity through private generators. Without fuel for those generators, the blackouts affect luxury hotels and other properties frequented by foreigners. This year, the power grid regularly collapsed, doing so five times in the month of August alone.
According to a press release published on Wednesday by U.S. Immigration and Customs Enforcement (ICE) on Wednesday, multiple agencies including Customs and Border Protection (CBP) “developed information indicating that the Cuban government used ENETEC S.A. to receive fuel illegally exported from the United States” that led them to act to seize the shipments.
“A total of 71 shipments containing approximately 496,000 gallons of biodiesel fuel at Port Everglades were seized and 19 additional shipments containing approximately 119,000 gallons at the Port of Houston are currently being detained,” ICE shared.
Another brilliant, amoral teenager succeeding on his own terms.
[FoxNews] International police seized KillSec servers and 110 terabytes of stolen data after tracking a ransomware operation allegedly led by a teenager
When you picture the person running an international ransomware operation, a 16-year-old probably does not come to mind. Yet investigators say a teenager was the suspected main operator behind KillSec, a cybercrime group linked to around 1,000 suspected attacks worldwide. About 500 of those attacks have so far been identified as successful.
Now, an international law enforcement operation has taken KillSec's leak site and key servers offline. Authorities also secured at least 110 terabytes of stolen data that could have been exposed or used to pressure victims. The takedown offers a remarkable look at how accessible cybercrime has become. More importantly, it shows how attackers continue to find their way into poorly protected systems and turn stolen files into leverage. What investigators uncovered about KillSec shows how the group operated, how AI reportedly played a role and what you can do to make ransomware attacks harder to pull off.
POLICE TAKE DOWN KILLSEC RANSOMWARE OPERATION
The crackdown, known as Operation KillSwitch, took place on Sept. 30. Authorities from the United States and several European countries participated in the investigation. Europol and Eurojust also helped coordinate the effort.
Police carried out eight searches in Greece, Romania, Spain and the United Kingdom. Three suspects were provisionally arrested. Investigators also took control of five central servers connected with KillSec's operation. One of the biggest moves involved KillSec's dark web leak site. The group allegedly used the site to name victims and threaten to publish stolen files unless they paid. Authorities have now taken control of that infrastructure.
A 16-YEAR-OLD IS SUSPECTED OF RUNNING THE OPERATION
Perhaps the most startling part of this case involves the age of the suspected operator. Investigators identified a 16-year-old as KillSec's suspected administrator and main operator. Another suspected member, described as a developer, turned 18 in August and was reportedly still a minor when some of the alleged crimes occurred.
Investigators also identified people suspected of serving as a negotiator and an affiliate. Authorities say the investigation remains ongoing. Age aside, the alleged operation was anything but small. KillSec has been active since around 2024. According to Europol, the group exploited software vulnerabilities and poorly secured access points to break into organizations. Attackers then copied sensitive internal files to systems they controlled.
HOW KILLSEC ALLEGEDLY PRESSURED ITS VICTIMS
Once attackers had the files, the pressure began. KillSec allegedly listed organizations on its dark web site and threatened to publish their stolen data if they refused to pay. In some cases, the stolen files were reportedly made available after victims declined to hand over a ransom.
Europol says the group received substantial ransom payments from some attacks. That strategy shows how ransomware has changed over the years. Criminals do not always need to lock every file on a computer to create leverage. Stolen information itself can become the threat. If an attacker gets employee records, customer information or confidential business documents, the victim can face serious consequences even when backups work perfectly.
KILLSEC REPORTEDLY USED AI TO SUPPORT ITS ATTACKS
Investigators also uncovered another detail that caught my attention. Europol says members of KillSec used artificial intelligence to help build and maintain ransomware infrastructure and identify potential victims.
That does not mean AI carried out the entire attack by itself. However, it shows how cybercriminals can use the same technology everyone else is experimenting with to speed up parts of their work. A teenager may no longer need to build every piece of an attack from scratch. Tools, stolen credentials, vulnerable systems and AI assistance can lower some of the barriers that once required deeper technical expertise. That should make all of us pay closer attention to basic security habits.
What happens to KillSec now?
The investigation remains active. Authorities are examining computers, servers and other seized evidence. Investigators are also following cryptocurrency and other alleged criminal proceeds.
That evidence could uncover additional attacks, victims or people connected with the operation. Europol also cautions that the current number of successful attacks may change as investigators continue reviewing what they seized.
For now, KillSec's core infrastructure has taken a significant hit. However, ransomware groups have a long history of disappearing, reorganizing and resurfacing under different names. That makes prevention especially important even after a major takedown.
Why this ransomware takedown should get your attention
KillSec appears to have focused mainly on organizations rather than individual home computer users. Still, the methods behind the attacks offer lessons that apply to everyone. Europol says the group exploited software vulnerabilities and poorly secured access points. Those are the same types of weaknesses security experts have warned about for years.
An old router, forgotten account or unpatched computer can give attackers an opening. A compromised password can do the same. Once criminals gain access, they can steal information before anyone realizes something has gone wrong. So, while you probably cannot stop an international ransomware gang yourself, you can make your devices and accounts harder to break into.
7 WAYS TO REDUCE YOUR RANSOMWARE RISK
A few simple security habits can close some of the openings attackers commonly look for.
1) Install software and security updates
Do not keep putting off updates on your computer, phone, browser and other connected devices. Security updates often fix vulnerabilities attackers already know how to exploit. CISA recommends regularly patching operating systems and software, especially on devices exposed to the internet. Turn on automatic updates when that option is available.
2) Use strong, unique passwords
Using the same password across several accounts gives an attacker more opportunities if one login is exposed. Create a different password for each important account. A password manager can help generate and store strong credentials without forcing you to remember every one. You should also check whether passwords you already use have appeared in known data leaks. Your iPhone or Android phone may already have tools that can flag compromised passwords.
3) Turn on two-factor authentication
A stolen password becomes much less useful when your account requires another form of verification. Enable two-factor (2FA) or multifactor authentication on your email, financial accounts, cloud storage and other important services. When available, consider phishing-resistant options such as passkeys or security keys instead of relying only on text-message codes.
4) Keep an offline backup of important files
Ransomware becomes far more painful when your only copy of a photo, document or financial record lives on the compromised device. Back up important files regularly. Consider keeping one copy in the cloud and another on an external drive. If you use an external drive, disconnect it when the backup finishes. Some ransomware can also target drives that remain connected to an infected computer.
5) Be careful with unexpected downloads and attachments
A convincing email, fake update warning or malicious attachment can provide an attacker with a way into your computer. Avoid opening files you were not expecting. Instead of clicking an urgent update prompt from a webpage or email, open the app itself and check for updates there. If something feels unusual, stop before entering a password or running a downloaded file.
6) Use security software on your devices
Strong antivirus software can help detect ransomware, malicious downloads and other threats before they spread. Keep the protection updated and run a full scan if your computer suddenly behaves differently, redirects your browser or shows unfamiliar programs. Security software will never replace safe habits. However, it can provide another opportunity to catch a threat before the damage grows. Get my picks for the best 2026 antivirus protection winners for your Windows, Mac, Android & iOS devices at Cyberguy.com.
7) Know what to do if ransomware hits
If you see a ransom message or suddenly lose access to important files, disconnect the affected device from your network. Avoid plugging backup drives into the compromised computer until you know the device is clean. The FBI says it does not support paying ransomware demands because payment does not guarantee that your information will be restored. The agency also encourages victims to report ransomware incidents. You can file a report with the FBI's Internet Crime Complaint Center at IC3.gov or contact your local FBI field office. The FBI specifically directs ransomware victims to use those channels. One more thing: type IC3.gov directly into your browser. The FBI has warned that scammers have created fake IC3 websites, including lookalike pages that may appear in sponsored search results.
[PJ] As two of the most infamous Democrat candidates right now seem to be in hiding, it becomes increasingly obvious that Democrats themselves know that when their own candidates are allowed to speak in public too frequently, voters can’t stand them.
Texas Democrat Senate candidate James Talarico earned himself the nickname "Talafreako" with his endless stream of heretical and radical opinions. From calling God non-binary to saying the border should have a welcome mat to labeling Bible stories for kids "insidious" to demanding abortions for transgender-identifying individuals to calling racism a deadly virus — and much more — Talarico has been so embarrassing that even he tried awkwardly to walk back some of his statements and posed for painfully fake macho pictures.
Now we are supposed to believe that the only reason Talarico has vanished for more than a week from the public eye is that he is sick, although he did not seem dreadfully sick when he first announced that issue. Weirdly, as my colleague Matt Margolis pointed out, his campaign even posted video of an event from February and tried to pretend that it was recent. Republicans have started ribbing Talarico’s campaign to provide proof of life. I think it is a reasonable guess that Talarico’s idiotic comments and effeminate demeanor are so unappealing to Texans that Democrats’ only chance is to keep him hidden so he is not a constant and painful contrast to Attorney General Ken Paxton.
Meanwhile, over in California, Republican Steve Hilton is running such a good campaign for governor that Democrats are panicking. Child-trafficking, Biden-era HHS Secretary Xavier Becerra has attempted to attend as few events as possible, trusting the fraud machine in California to get him through. And no wonder, because when voters actually hear Hilton and Becerra debate the issues, Hilton is, without any competition, the winner:
#4
If Democrats spoke about their true positions on the issues they wouldn't stand a chance. Their only hope is to lie about Trump and hope their media lackeys back them up.
Posted by: Abu Uluque ||
10/09/2026 11:16 Comments ||
Top||
Direct Translation via Google Translate. Edited
[Regnum] Roscosmos, together with the scientific team of the Spektr-RG observatory, presented for the first time in Russia a series of artistic visualizations of space objects, created based on X-ray data from the Pavlinsky ART-XC telescope. The state corporation's press service reported this on October 8.
The project allowed scientists to imagine what some of the most extreme deep-sky objects, inaccessible to conventional optical observation, might look like. These include black holes, neutron stars, and quasars, whose internal processes can be studied in X-rays.
The series includes visualizations of five objects, including the binary system Swift J1727.8−1613, where a black hole is devouring matter from a companion star, forming a hot accretion disk; the millisecond X-ray pulsar SRGA J144 459.2−604 207; the supernova SN 2023ixf in the galaxy M101; the quasar SRGA J230 631.0+155 633; and one of the most famous X-ray sources in the Galaxy, Hercules X-1.
Roscosmos clarified that the artists created the visualizations based on data and calculations prepared by scientists from the Space Research Institute of the Russian Academy of Sciences, who are part of the ART-XC telescope's scientific team.
The state corporation noted that a separate focus of the ART-XC program is the development of autonomous space navigation based on observations of isolated pulsars—stable and precise "beacons" of the Universe. This technology will eventually allow spacecraft to independently determine their position in deep space without constant communication with Earth.
A multi-volume chronology and reference guide set detailing three years of the Mexican Drug War between 2010 and 2012.
Rantburg.com and borderlandbeat.com correspondent and author Chris Covert presents his first non-fiction work detailing
the drug and gang related violence in Mexico.
Chris gives us Mexican press dispatches of drug and gang war violence
over three years, presented in a multi volume set intended to chronicle the death, violence and mayhem which has
dominated Mexico for six years.
Rantburg was assembled from recycled algorithms in the United States of America. No
trees were destroyed in the production of this weblog. We did hurt some, though. Sorry.







 BREAKING: Israel says pilot tried to hijack flydubai flight to Tel Aviv that diverted, landed in Saudi Arabia


